SSH Session Timeout – TCP Keepalive
SSH sessions can sometimes disconnect unexpectedly after a period of inactivity, even when the remote server is still running and the network connection appears to be working properly. This behavior is often caused by idle connection timeouts enforced by firewalls, NAT devices, or other network components.
To prevent these unwanted disconnections, SSH provides several keepalive mechanisms that can be configured on either the SSH server or the client. These include TCP-level keepalives as well as SSH-level keepalive messages sent through the encrypted connection.
In this post, we will look at the differences between these mechanisms and how to configure them on Linux and Windows, including OpenSSH, PowerShell, PuTTY, and WinSCP, to keep idle SSH sessions connected.
Configure SSH Keepalives on the Server (sshd)
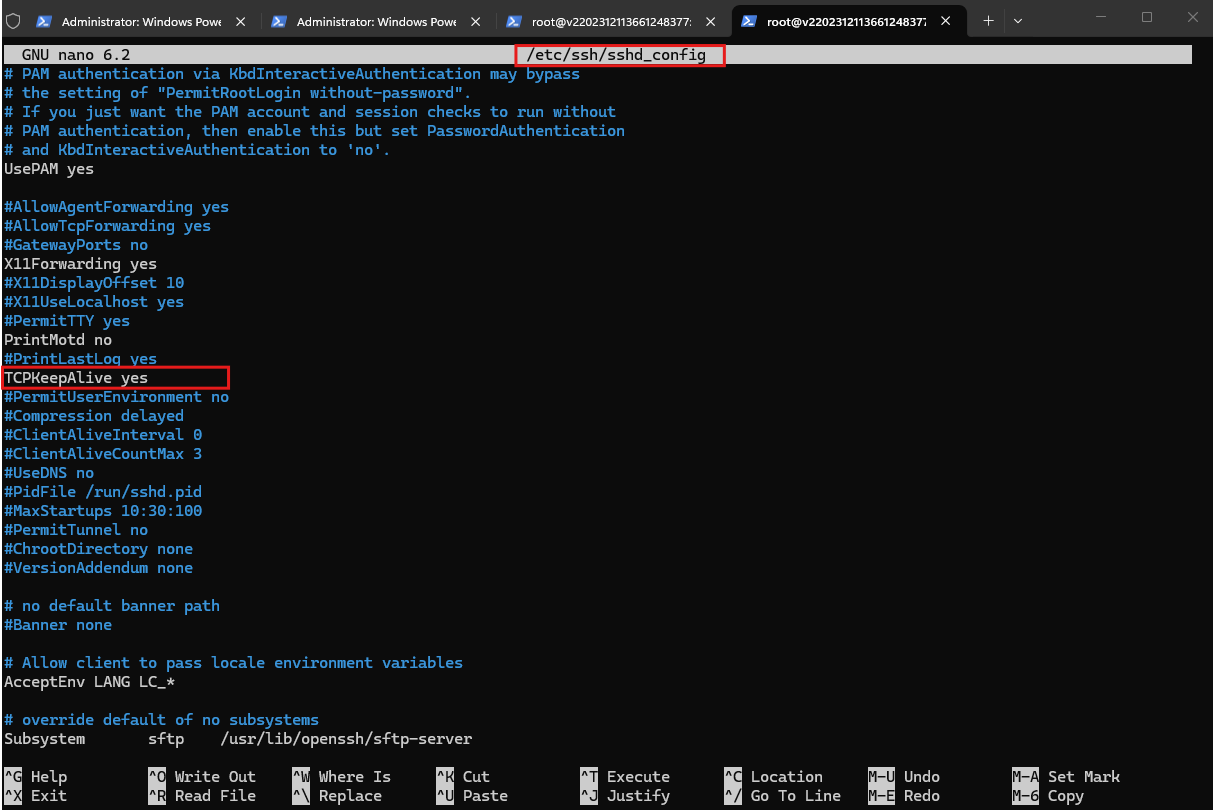
In case our ssh connection is permanently disconnected in idle state, we can enable TCP-Keepalive either on the ssh server or the client or on both.
To enable TCP-Keepalive on the ssh server, we can comment out the following line in /etc/ssh/sshd_config
TCPKeepAlive yes
Configure SSH Keepalives on the Linux Client (OpenSSH)
To enable TCP-Keepalive on the Linux client system wide, we can edit the /etc/ssh/ssh_config file and add the following entry.
The default value for
ServerAliveIntervalin OpenSSH client configuration is0.A value of
0disables sending keepalive packets entirely. When not explicitly defined in/etc/ssh/ssh_config(or~/.ssh/config), the SSH client will not send periodic encrypted null packets to maintain inactive connections, leaving idle connection timeouts strictly up to network firewalls, routers, or the server’sClientAliveIntervalsettings.
ServerAliveInterval 15

# 15 -> timeout interval in seconds after which if no data has been received from the server, ssh will send a message through the encrypted channel to request a response from the server.
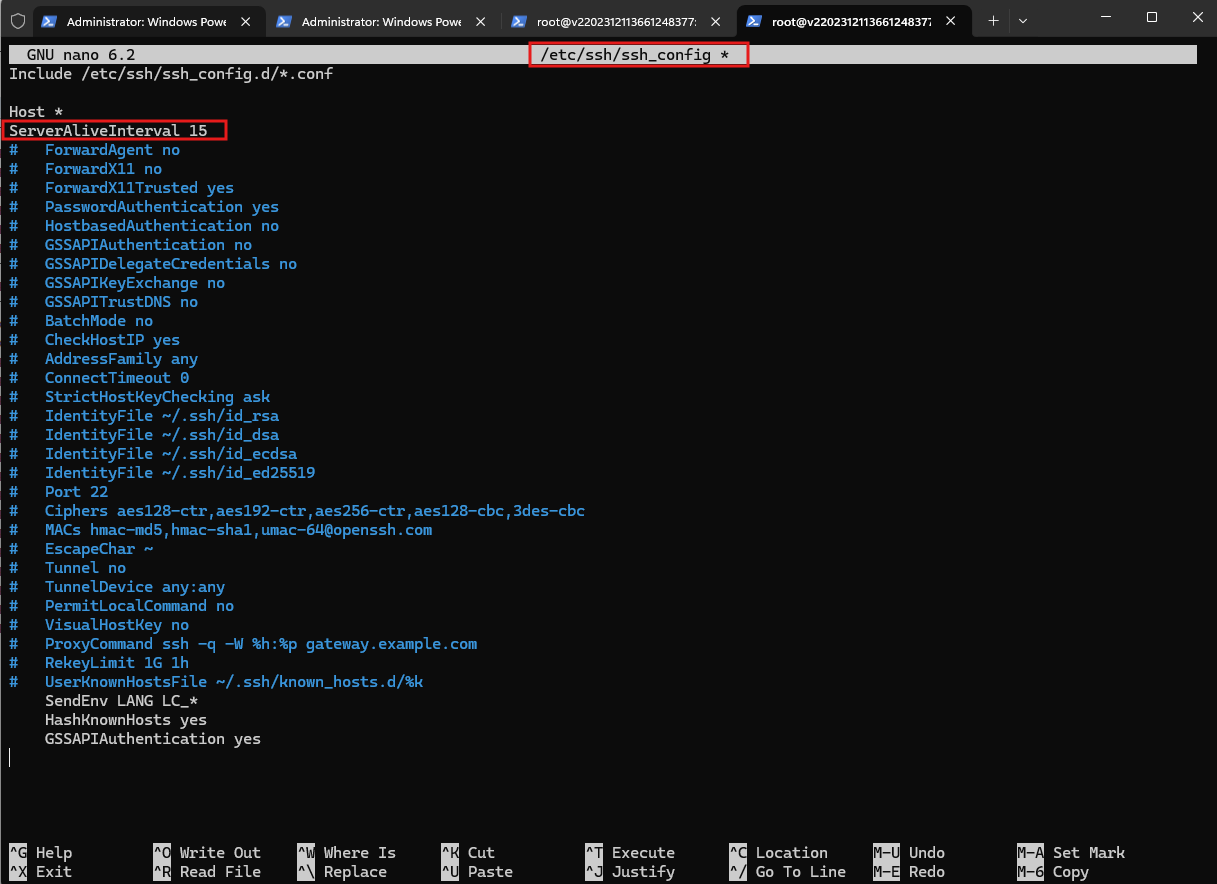
If we want to enable this only for a specific user, we can add the following lines into the user’s ssh config file located in /home/<username>/.ssh/config or only for the actual user by ~/.ssh/config.
If the config file doesn’t exists, simply create it.
Host *
ServerAliveInterval 15
Configure SSH Keepalives in PuTTY
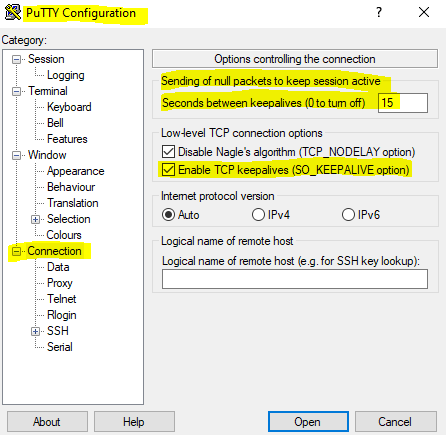
To enable TCP-Keepalive on the client (Putty), you can check Enable TCP keepalives (SO_KEEPALIVE option) as follows and further set the seconds to send null packets to the server to keep the session active.
Configure SSH Keepalives in WinSCP
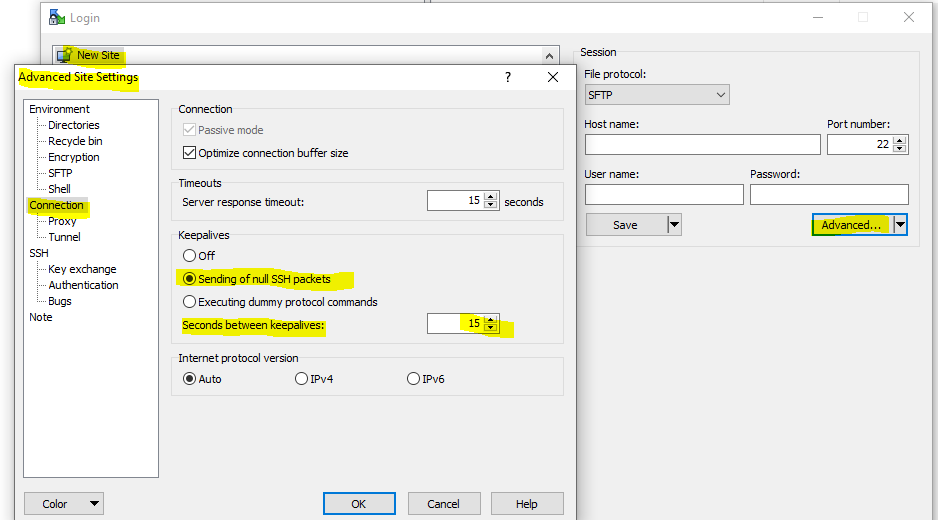
For WinSCP use the following settings in Advanced for the specific ssh connection.
Sending of null SSH packets
Configure SSH Keepalives on Windows using PowerShell
When using the built-in OpenSSH client in Windows PowerShell, we can also configure SSH-level keepalives to prevent idle SSH sessions from being disconnected by firewalls, NAT devices, or other network components.
For a single connection, we can use the following command:
ssh -o ServerAliveInterval=15 -o ServerAliveCountMax=3 user@server.example.com
- ServerAliveInterval 15 – Sends an encrypted SSH keepalive request after 15 seconds without receiving data from the server.
- ServerAliveCountMax 3 – Terminates the connection after three consecutive unanswered keepalive requests.
Configure SSH Keepalives Permanently
Instead of specifying these parameters every time, we can configure them permanently in our local SSH client configuration file.
On Windows, this file is located at:
$env:USERPROFILE\.ssh\config
Open it using:
notepad $env:USERPROFILE\.ssh\config
For example, we can define the following configuration:
Host myserver
    HostName server.example.com
    User username
    ServerAliveInterval 15
    ServerAliveCountMax 3
We can now connect simply by running:
ssh myserver
Alternatively, we can apply the keepalive settings to all SSH connections by using the wildcard Host *:
Host *
    ServerAliveInterval 15
    ServerAliveCountMax 3
Note: Unlike
TCPKeepAlive, which operates at the TCP level,ServerAliveIntervalsends keepalive messages through the encrypted SSH channel. This makes it generally more suitable for preventing idle connection timeouts.
For more information about configuring SSH connections through the local SSH configuration file, including SSH jump hosts, see my following article.
Configure SSH Keepalives with Public/Private Key Authentication
When using SSH public/private key authentication, we can additionally specify the path to our private key using the IdentityFile directive.
Host myserver
    HostName server.example.com
    User username
    IdentityFile ~/.ssh/id_ed25519
    IdentitiesOnly yes
    ServerAliveInterval 15
    ServerAliveCountMax 3
- IdentityFile – Specifies the private key used for authentication. The corresponding public key must be configured on the SSH server.
- IdentitiesOnly yes – Restricts authentication to explicitly configured identities instead of trying additional keys offered by the SSH agent.
- ServerAliveInterval 15 – Sends encrypted SSH keepalive requests after 15 seconds of inactivity.
- ServerAliveCountMax 3 – Disconnects after three consecutive unanswered keepalive requests.
We can now establish the SSH connection using:
ssh myserver
The OpenSSH client automatically uses the configured hostname, username, private key, and keepalive settings.
Note: The example uses the default Ed25519 private key filename. If your private key has a different name or location, adjust the
IdentityFiledirective accordingly.
Links
sshd_config — OpenSSH daemon configuration file
https://man7.org/linux/man-pages/man5/sshd_config.5.htmlssh_config — OpenSSH client configuration file
https://man.openbsd.org/ssh_configOpenSSH Server configuration for Windows Server and Windows
https://learn.microsoft.com/en-us/windows-server/administration/openssh/openssh-server-configurationTutorial: SSH in Windows Terminal
https://learn.microsoft.com/en-us/windows/terminal/tutorials/ssh